AI in Cybersecurity: US Data Protection Measures for 2026
AI in Cybersecurity: 4 Proactive Measures for US Data Protection in 2026
In an increasingly interconnected world, the security of digital information has become paramount. For the United States, safeguarding critical infrastructure, government secrets, corporate intellectual property, and individual privacy is not merely a technical challenge but a matter of national security and economic stability. As we hurtle towards 2026, the landscape of cyber threats is evolving at an unprecedented pace, driven by sophisticated adversaries and the proliferation of advanced attack vectors. This escalating threat environment necessitates a fundamental shift in our approach to cybersecurity, moving from reactive defense to proactive, intelligent prevention. This is where Artificial Intelligence (AI) emerges as a transformative force, offering capabilities that far surpass traditional security measures.
The integration of AI cybersecurity US strategies is no longer a futuristic concept but a present-day imperative. AI’s ability to process vast quantities of data, identify complex patterns, and make real-time decisions positions it as an indispensable tool in the ongoing battle against cyber adversaries. From detecting nascent threats before they escalate to automating defensive responses, AI promises a more resilient and adaptive cybersecurity posture. This article will delve into four pivotal proactive measures leveraging AI that the US must prioritize to bolster its data protection capabilities by 2026. These measures are designed not only to counter current threats but also to anticipate and neutralize future challenges, ensuring a robust and impenetrable digital frontier for the nation.
The Evolving Cyber Threat Landscape and AI’s Role
Before we explore specific AI-driven measures, it’s crucial to understand the context. The cyber threat landscape is a dynamic and hostile environment. Nation-state actors, organized cybercrime groups, and even individual hackers are constantly developing new tactics, techniques, and procedures (TTPs). These range from highly sophisticated zero-day exploits and advanced persistent threats (APTs) to widespread phishing campaigns and ransomware attacks that can cripple industries and public services. The sheer volume and velocity of these attacks often overwhelm traditional human-centric security operations centers (SOCs), leading to delayed responses and increased vulnerability.
Moreover, the rise of AI itself presents a dual challenge. While AI is a powerful defensive tool, it can also be weaponized by adversaries to create more effective malware, automate reconnaissance, and launch highly targeted attacks with unprecedented speed and scale. This ‘AI arms race’ in cybersecurity underscores the urgency for the US to not only adopt AI for defense but to do so strategically and comprehensively.
AI’s fundamental advantage lies in its capacity for machine learning (ML), natural language processing (NLP), and deep learning (DL). These capabilities enable AI systems to:
- Analyze massive datasets: AI can sift through petabytes of network traffic, log data, and threat intelligence feeds much faster and more accurately than humans.
- Identify anomalies and patterns: It can detect subtle deviations from normal behavior that might indicate an attack, even if the attack signature is unknown.
- Automate responses: AI can initiate defensive actions, such as isolating compromised systems or blocking malicious traffic, in milliseconds, minimizing damage.
- Learn and adapt: AI systems continuously learn from new data and threats, improving their effectiveness over time without constant human reprogramming.
By harnessing these capabilities, the US can move beyond simply reacting to breaches and instead build a truly proactive and predictive defense system. The focus on AI cybersecurity US initiatives is therefore not just about technology adoption, but about establishing a new paradigm of digital defense.
Measure 1: Enhanced AI-Driven Anomaly Detection and Predictive Threat Intelligence
One of the most critical applications of AI in cybersecurity is its ability to detect anomalies and predict potential threats before they materialize into full-blown attacks. Traditional intrusion detection systems (IDS) rely heavily on signature-based detection, which is effective against known threats but often fails against novel or polymorphic malware. AI, particularly machine learning algorithms, offers a significant leap forward by establishing baselines of normal network and user behavior and then flagging any significant deviations.
How AI Enhances Anomaly Detection:
- Behavioral Analytics: AI models can analyze user behavior (User and Entity Behavior Analytics – UEBA) and network traffic patterns to identify unusual activities. For instance, an employee suddenly accessing sensitive files outside working hours or from an unusual location would trigger an alert. Similarly, a server exhibiting abnormal outbound data transfers could indicate data exfiltration.
- Unsupervised Learning: This type of AI can discover hidden patterns and structures in data without explicit programming, making it ideal for identifying zero-day exploits or previously unseen attack vectors that don’t match any known signatures.
- Contextual Analysis: AI can correlate events across different security layers – endpoints, networks, applications, and cloud environments – to build a comprehensive picture of an evolving threat. A seemingly innocuous event on one system might become highly suspicious when combined with other indicators detected elsewhere.
Predictive Threat Intelligence:
Beyond simply detecting anomalies, AI can transform raw threat data into actionable, predictive intelligence. By analyzing global threat feeds, dark web activity, geopolitical events, and even social media trends, AI can forecast potential attack vectors and identify adversaries’ likely targets. This enables organizations to harden their defenses proactively in anticipation of specific threats.
- Vulnerability Prioritization: AI can assess the likelihood of specific vulnerabilities being exploited based on current threat intelligence and the organization’s unique attack surface, allowing security teams to patch and mitigate the most critical risks first.
- Adversary Profiling: By analyzing past attack campaigns and adversary TTPs, AI can help create detailed profiles of threat actors, including their motivations, capabilities, and preferred methods, aiding in proactive defense planning.
The US government, critical infrastructure operators, and private sector entities must invest heavily in AI-powered anomaly detection and predictive threat intelligence platforms. These systems should be integrated across various sectors, allowing for a more unified and informed national cybersecurity posture. The goal is to move from a reactive ‘whack-a-mole’ approach to a proactive, ‘predict and prevent’ strategy, significantly bolstering AI cybersecurity US capabilities.
Measure 2: Automating Incident Response and Remediation with AI
Even with the most advanced detection systems, breaches are an unfortunate reality. The speed at which an organization can respond to and remediate an incident often determines the extent of the damage. Traditional incident response (IR) processes are often manual, labor-intensive, and slow, relying on human analysts to triage alerts, investigate, and execute remediation steps. This delay can allow attackers to deepen their foothold, exfiltrate more data, or cause greater disruption.
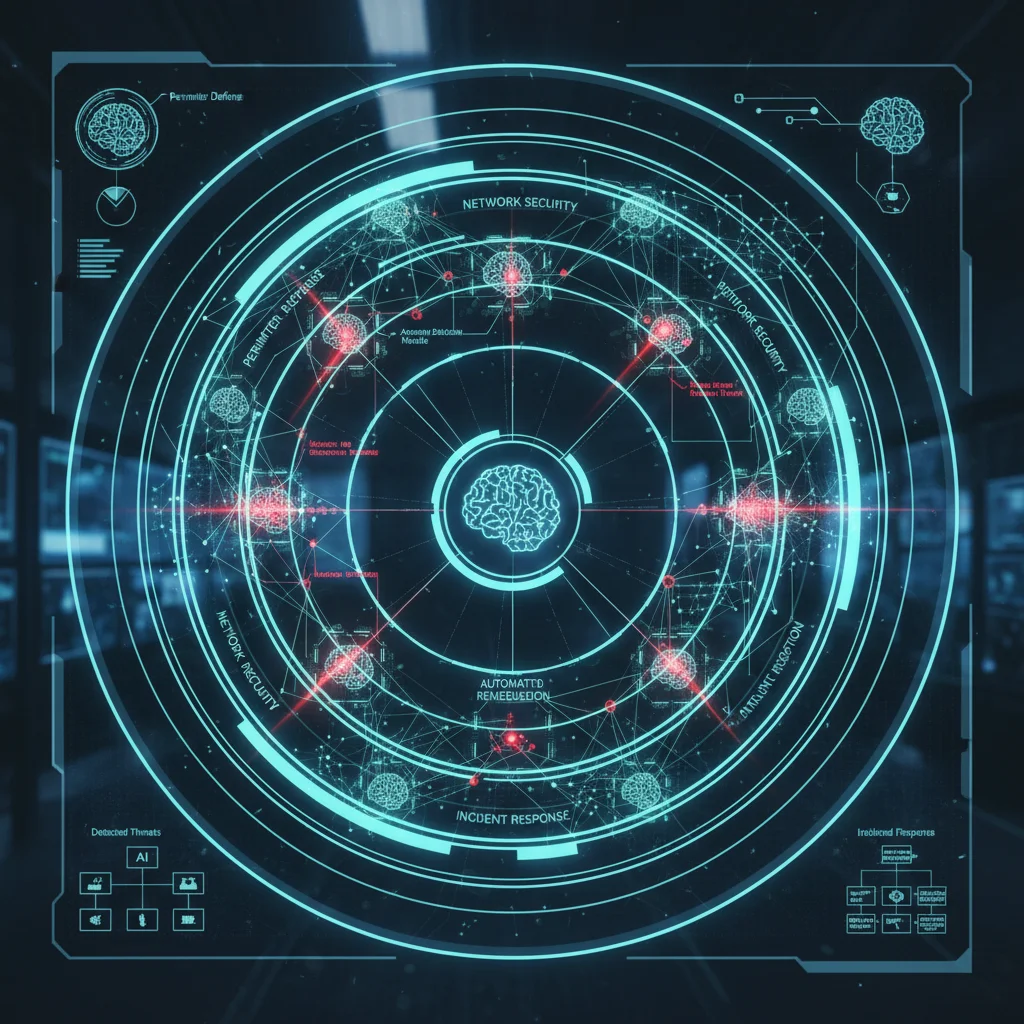
AI, coupled with Security Orchestration, Automation, and Response (SOAR) platforms, can dramatically accelerate and improve the efficiency of incident response. By automating repetitive tasks and providing intelligent recommendations, AI empowers security teams to respond to threats in machine time, not human time.
Key AI Applications in Incident Response:
- Automated Alert Triage: AI can analyze and prioritize security alerts from various sources (SIEM, EDR, firewalls) by correlating events, enriching data with threat intelligence, and assessing the true risk level. This reduces alert fatigue for analysts and ensures critical incidents are addressed first.
- Playbook Execution: AI can trigger predefined playbooks for common incident types. For example, if ransomware is detected, AI can automatically isolate the infected endpoint, block malicious IP addresses, revert to a clean backup, and notify relevant stakeholders.
- Threat Hunting and Investigation: AI can assist human threat hunters by processing vast amounts of log data to identify subtle indicators of compromise (IoCs) and provide context to ongoing investigations, reducing the time to discovery and containment.
- Malware Analysis: AI can perform rapid, automated analysis of suspicious files in a sandbox environment, identifying their behavior and characteristics without human intervention, thus speeding up the creation of new threat signatures.
The implementation of AI-driven automated incident response systems across federal agencies and critical infrastructure is paramount. This requires not only the deployment of appropriate technologies but also the development of standardized playbooks and protocols that AI systems can execute. Furthermore, human oversight and intervention will remain crucial, especially for complex or novel incidents, but AI will serve as a powerful force multiplier, freeing up human experts to focus on strategic analysis and decision-making. This proactive automation is a cornerstone of enhancing AI cybersecurity US defense capabilities.
Measure 3: Securing Critical Infrastructure and Supply Chains with AI
The US critical infrastructure – including energy grids, water treatment facilities, transportation networks, and financial systems – represents a prime target for cyber adversaries. Attacks on these systems can have catastrophic consequences, disrupting essential services, endangering lives, and destabilizing the economy. Moreover, the increasing interconnectedness of these systems, often relying on complex global supply chains, creates numerous vulnerabilities.
AI offers unique capabilities to secure these vital assets by providing continuous monitoring, predicting failures, and defending against sophisticated attacks that could exploit operational technology (OT) and industrial control systems (ICS).
AI for Critical Infrastructure Protection:
- Anomaly Detection in OT/ICS: AI can monitor the unique protocols and behaviors of OT/ICS networks, detecting abnormal commands, unauthorized access attempts, or unusual operational parameters that could indicate an attack or system malfunction.
- Predictive Maintenance and Resilience: By analyzing sensor data and operational logs, AI can predict equipment failures, allowing for proactive maintenance and preventing disruptions that could be exploited by attackers. It can also help design more resilient systems that can withstand and recover from cyber-physical attacks.
- Real-time Threat Monitoring: AI can provide a unified view of security across IT and OT environments, correlating events to identify sophisticated attacks that bridge both domains.
AI for Supply Chain Security:
The software supply chain, in particular, has become a significant attack vector. Adversaries inject malicious code into legitimate software components or compromise trusted vendors to gain access to downstream users. AI can play a crucial role in mitigating these risks:
- Code Analysis and Vulnerability Scanning: AI-powered tools can automatically scan source code and binaries for vulnerabilities, backdoors, and malicious injections, even in third-party components.
- Behavioral Monitoring of Software: AI can monitor the behavior of software components during development and deployment, flagging any unexpected actions or deviations from established baselines that might indicate compromise.
- Vendor Risk Assessment: AI can analyze vast amounts of data on vendors, including their security posture, past incidents, and compliance records, to provide a more accurate and continuous assessment of supply chain risk.
For 2026, the US must mandate and facilitate the adoption of AI-driven security solutions across all critical infrastructure sectors and their associated supply chains. This will require public-private partnerships, robust regulatory frameworks, and significant investment in research and development to tailor AI solutions to the unique challenges of OT/ICS environments. Strengthening AI cybersecurity US in these areas is non-negotiable for national resilience.
Measure 4: Developing AI-Powered Cyber Workforce Training and Threat Emulation
Even the most advanced AI systems are only as effective as the human experts who design, deploy, and manage them. The current cybersecurity workforce shortage in the US is a critical vulnerability. To effectively leverage AI for data protection by 2026, the nation must invest in developing an AI-literate cyber workforce capable of interacting with, optimizing, and overseeing these sophisticated systems. Furthermore, AI can be a powerful tool for training and for testing defenses through advanced threat emulation.
AI for Workforce Development:
- Personalized Training Programs: AI can tailor cybersecurity training modules to individual skill gaps and learning styles, making education more efficient and effective. It can identify areas where an analyst struggles and provide targeted resources.
- Simulated Cyber Ranges: AI-powered cyber ranges can create highly realistic and dynamic attack scenarios for training. These simulations can adapt in real-time based on trainee actions, providing an unparalleled learning experience for incident response, threat hunting, and forensics.
- Automated Skill Assessment: AI can objectively assess the performance of cybersecurity professionals in simulated environments, identifying strengths and weaknesses and tracking progress.
- Knowledge Management: AI can consolidate and make accessible vast amounts of cybersecurity knowledge, including threat intelligence, best practices, and incident reports, helping new and experienced analysts alike.
AI for Advanced Threat Emulation and Red Teaming:
To truly test the robustness of AI-driven defenses, the US needs AI-powered tools that can act as sophisticated adversaries. This involves:
- AI-Driven Attack Generation: AI can generate highly realistic and novel attack vectors, including polymorphic malware and advanced phishing campaigns, to challenge existing defenses. This allows organizations to discover vulnerabilities before real attackers do.
- Automated Red Teaming: AI can execute automated red team exercises, continuously probing an organization’s network for weaknesses, identifying potential entry points, and testing the effectiveness of security controls.
- Adversarial AI for Defensive Improvement: By using AI to understand how adversaries might use AI to bypass defenses, the US can develop more resilient AI-powered security solutions. This involves training defensive AI systems against AI-generated attacks.
By 2026, the US must establish national AI cybersecurity academies and incentivize AI and cybersecurity education at all levels. Furthermore, federal agencies and critical infrastructure operators should regularly engage in AI-driven threat emulation exercises to continually stress-test and improve their defenses. This dual approach – enhancing human capabilities with AI and using AI to challenge those capabilities – is essential for a truly resilient AI cybersecurity US framework.
Challenges and Ethical Considerations
While the promise of AI in cybersecurity is immense, its widespread adoption is not without challenges and ethical considerations. These must be addressed proactively to ensure responsible and effective deployment:
- Data Privacy and Bias: AI systems require vast amounts of data to learn. Ensuring this data is collected and used ethically, without perpetuating biases or infringing on privacy rights, is crucial.
- Explainable AI (XAI): The ‘black box’ nature of some AI models can make it difficult for human analysts to understand why a particular decision was made. For critical security decisions, explainability is vital for trust and accountability.
- Adversarial AI Attacks: Attackers can attempt to ‘poison’ AI training data or craft inputs specifically designed to trick AI models into misclassifying threats or legitimate activities. Defending against these adversarial attacks is an evolving area of research.
- Talent Gap: While AI can augment the workforce, a significant shortage of professionals skilled in both cybersecurity and AI remains.
- Regulatory Frameworks: Developing appropriate regulations and standards for AI in cybersecurity, balancing innovation with security and privacy, will be a complex but necessary task.
Addressing these challenges requires a multi-faceted approach involving government policy, industry collaboration, academic research, and public discourse. The goal is to maximize the benefits of AI cybersecurity US efforts while mitigating potential risks.
Conclusion: A Resilient Digital Future for the US with AI
The journey to robust US data protection by 2026 is inextricably linked to the strategic and comprehensive integration of Artificial Intelligence into every facet of the nation’s cybersecurity architecture. The four proactive measures discussed – enhanced AI-driven anomaly detection and predictive threat intelligence, automating incident response and remediation, securing critical infrastructure and supply chains with AI, and developing AI-powered cyber workforce training and threat emulation – form the pillars of a forward-looking defense strategy.
By embracing these AI-driven approaches, the US can move beyond merely reacting to cyber threats and instead establish a truly predictive, adaptive, and resilient cybersecurity posture. This will not only safeguard sensitive data and critical systems but also reinforce national security, protect economic interests, and preserve the privacy of its citizens. The time for hesitant steps is over; a bold, integrated, and ethical commitment to AI cybersecurity US is essential to secure the digital future of the nation.
The implementation of these measures requires sustained investment, strong public-private partnerships, continuous research and development, and a commitment to nurturing a highly skilled cyber workforce. As cyber threats continue to evolve in sophistication and scale, AI offers the only viable path to staying ahead of adversaries. By 2026, the US has the opportunity to lead the world in AI-powered data protection, setting a new standard for national cybersecurity resilience.